About me
Senior DevOps Engineer with 10+ years of experience, passionate about cybersecurity, automation, optimizing workflows, implementing CI/CD pipelines and ensuring systems reliability.
Always eager to explore new technologies and improve existing processes for scalability and performance. Actively involved in security research, vulnerability assessment and secure software delivery. I believe in continuous learning, knowledge sharing and fostering a DevSecOps culture.
DevOps experience
SAP Commerce Cloud (SAP Hybris)
- Administered B2C and B2B storefronts for retail companies, ensuring scalability, high availability and resilience during peak traffic periods such as Black Friday, including bot and crawler management
- Administered, maintained and optimized SAP Commerce Cloud (Hybris) environments across Development, QA, Staging and Production
- Managed deployments on private cloud and AWS Linux-based infrastructure, including full platform and Java version upgrades
- Handled build processes using Ant, including deployment management, clustering configurations and platform properties
- Performed Tomcat tuning and JVM-level optimizations (heap memory, thread pools, GC settings)
- Executed migrations from private cloud to AWS and from on-premise infrastructure to SAP Commerce Cloud (CCv2)
DevOps technical skills 10+ years
Cloud
AWS: EC2, S3, EFS, RDS, CloudFront, WAF, Lambda, Backup
Edge & bot protection
Cloudflare Enterprise (Bot Management, WAF), AWS CloudFront, AWS WAF
CI/CD
Jenkins, GitHub Actions, GitLab CI, AWS CodePipeline, CodeBuild
Containers
Docker, Kubernetes, EKS, ECS, Argo CD
Infrastructure as Code
Terraform
Observability
Prometheus, Grafana, Loki, Alloy, ELK, CloudWatch, Nagios, PagerDuty
Operating systems
AL2, AL2023, CentOS, Ubuntu, Windows
Data & messaging
MySQL, PostgreSQL, MongoDB, Redis, Kafka (MSK), Solr
Scripting
Bash, Python, PowerShell
Full details
- Administered and maintained Linux/Unix (AL2, AL2023, CentOS, Ubuntu etc.) and Windows environments, ensuring system stability, security and reliability
- Performed operating system and software upgrades while maintaining platform integrity and minimizing service disruptions
- Designed, deployed and managed AWS cloud infrastructure, including EC2, S3, EFS, RDS and related services
- Built and maintained CI/CD pipelines using Jenkins, AWS CodePipeline, GitHub Actions and GitLab CI
- Managed Git-based development workflows, including GitHub and GitLab runners
- Configured and optimized web infrastructure, including Nginx, Apache, reverse proxies and load balancing solutions
- Implemented and managed CDN integrations using AWS CloudFront and Cloudflare to improve performance and global content delivery
- Developed backup and disaster recovery solutions using AWS Backup, automated snapshots, AMIs and rsnapshot
- Built monitoring, alerting and observability platforms using Prometheus, Grafana, Nagios, CloudWatch, ELK Stack, PagerDuty and CloudWatch Logs
- Automated operational tasks and infrastructure management through Bash, Python, PowerShell scripting and AWS Lambda
- Containerized applications with Docker and managed Kubernetes workloads using EKS, ECS and Argo CD
- Provisioned and managed cloud infrastructure using Terraform and Infrastructure as Code (IaC) principles
- Configured and maintained secure VPN solutions, including OpenVPN and WireGuard
- Administered MySQL, PostgreSQL and MongoDB databases, including performance optimization and maintenance
- Supported Java and Node.js microservices using Maven, AWS CodeArtifact and AWS CodeBuild
- Implemented static code analysis and quality checks using SonarQube
- Configured and maintained integrations with Solr, Kafka (Amazon MSK), Redis and third-party platforms
- Implemented AWS WAF protections, including anti-bot and anti-crawling mechanisms for public-facing applications
- Optimized web performance to improve page load speed and user experience
- Administered and maintained WordPress environments and related infrastructure
Certifications
AWS Certified DevOps Engineer – Professional
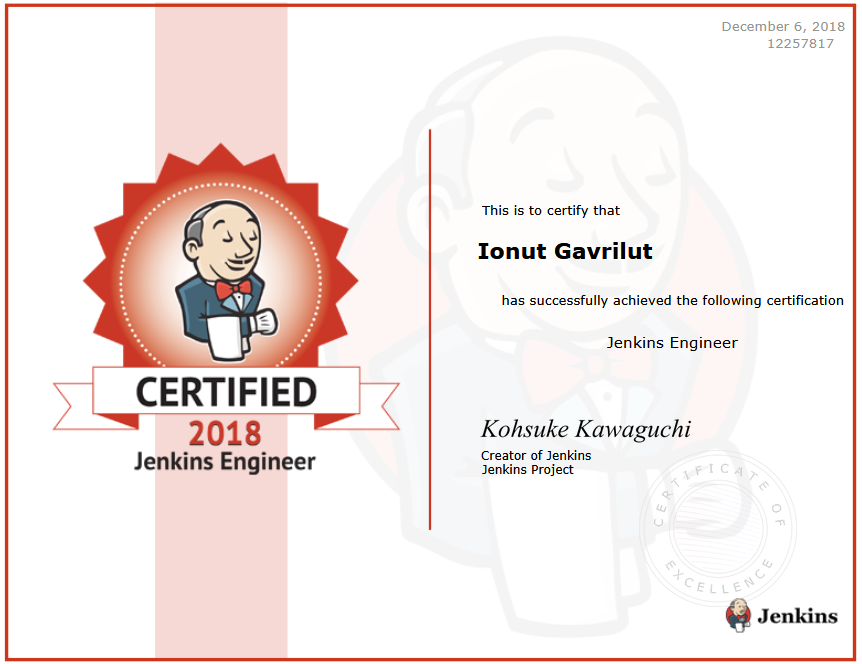
Certified Jenkins Engineer (CJE)
Previous certifications
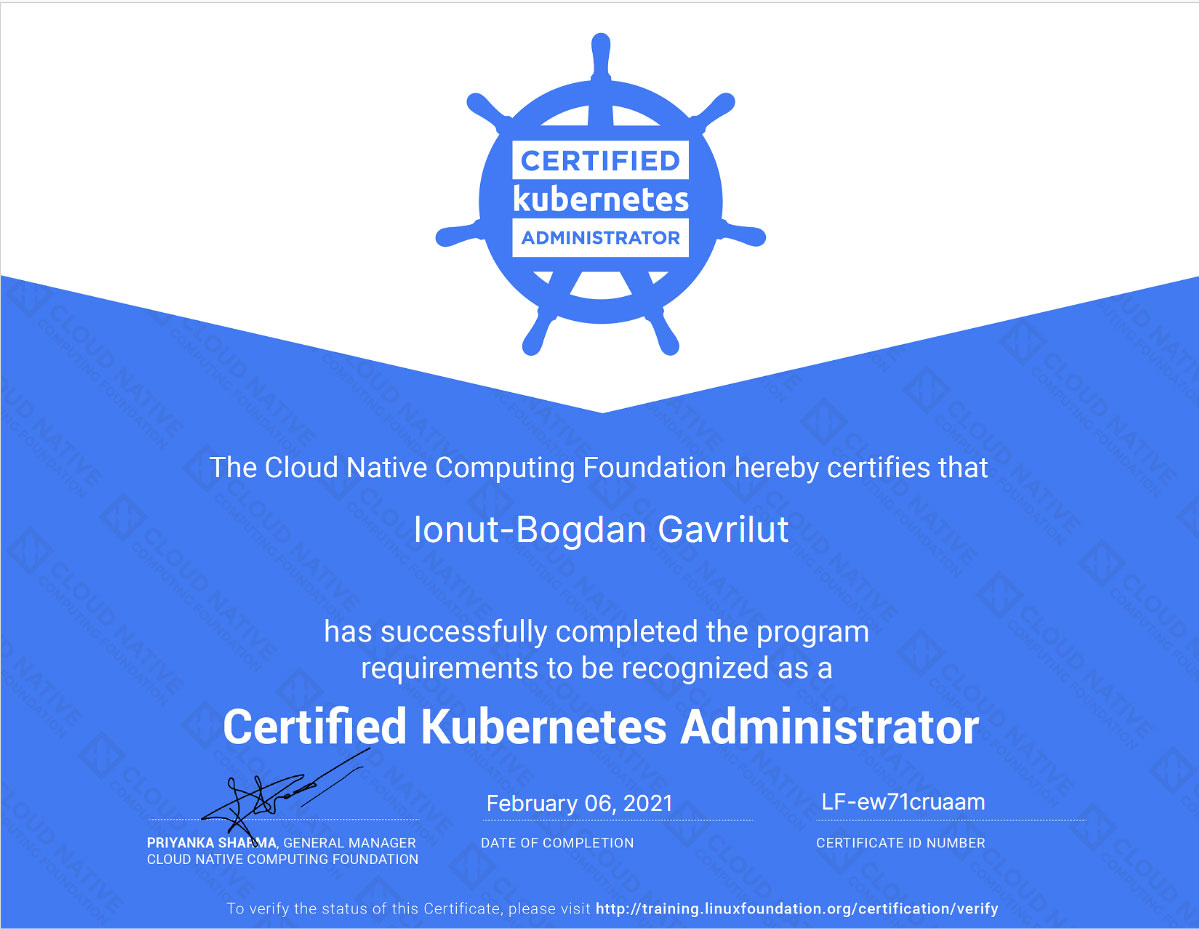
Certified Kubernetes Administrator (CKA)
Security research
- Reported critical security vulnerabilities in web applications to over 100 organizations, including major multinational companies (such as Walmart, Nestlé and Sony) and government institutions, through responsible disclosure, bug bounty and official vulnerability disclosure programs
- Conducted web application security assessments using Burp Suite Professional, identifying vulnerabilities such as XSS, IDOR, authentication weaknesses and access control issues
- Performed manual penetration testing of web applications following the OWASP Top 10
- Performed vulnerability assessments, attack surface analysis and security validation using Nessus and custom security testing methodologies
- Performed reconnaissance and attack surface mapping to identify exposed assets, hidden endpoints and potential attack vectors using Nmap, ffuf and Subfinder
Certifications
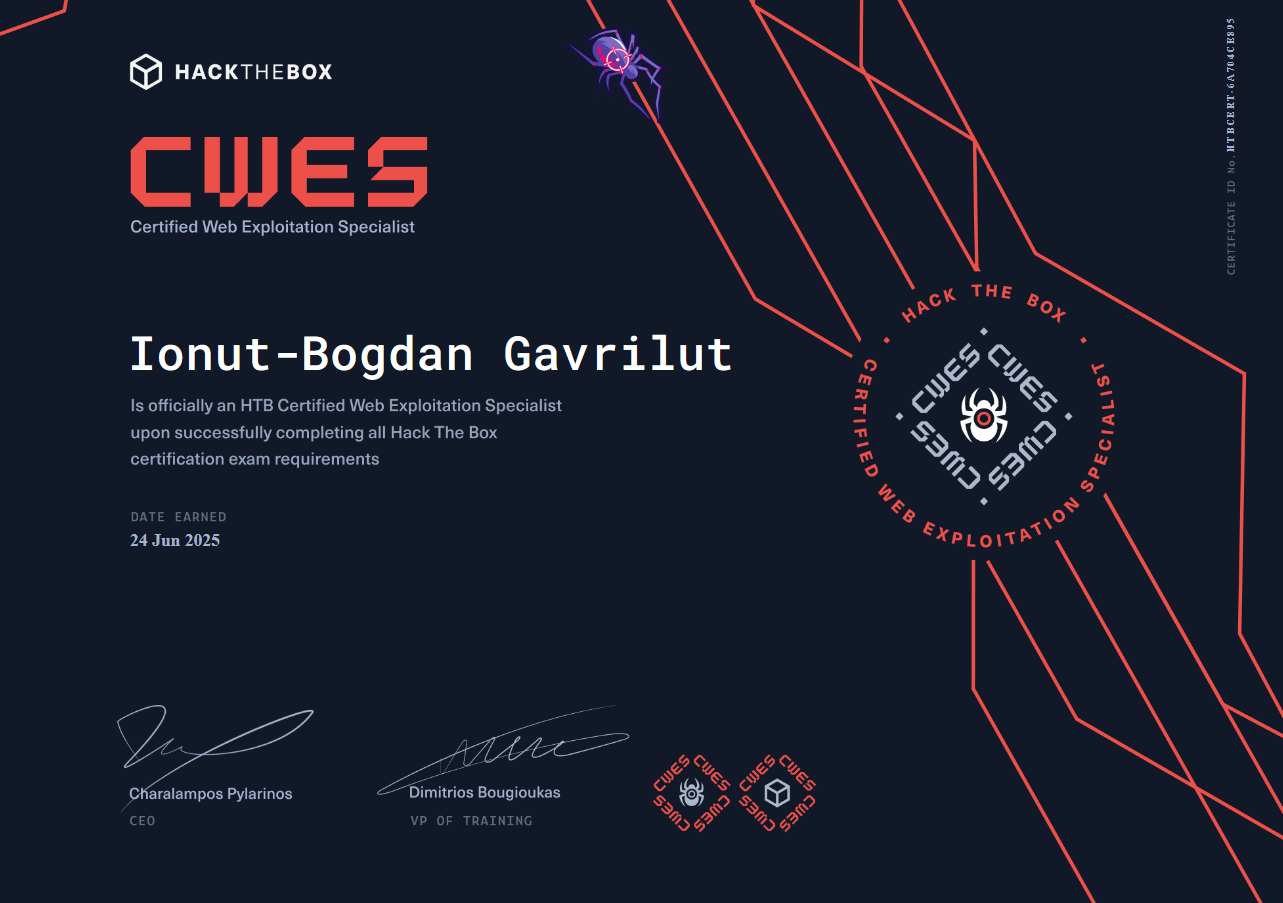
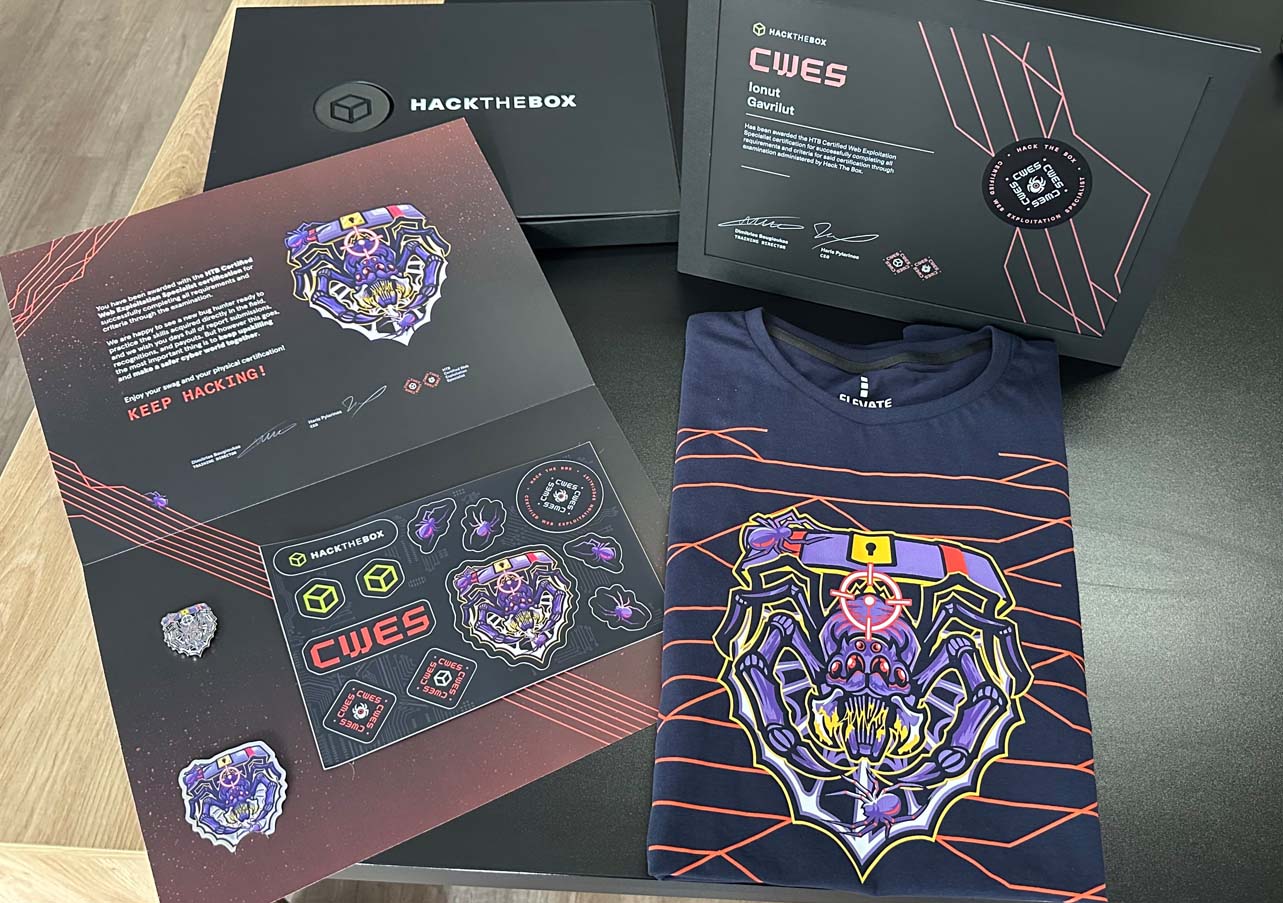
Certified Web Exploitation Specialist (CWES)
Scored 100/100 in a 7-day hands-on web exploitation assessment and delivered a 90-page professional penetration testing report.
Platforms
Halls of fame & acknowledgements
A selection of public acknowledgements from companies for identifying and reporting security vulnerabilities through responsible disclosure programs.
Also rewarded by Walmart, Coca-Cola, Red Bull, Nestlé, Pfizer, Sony, John Deere, Henkel and others.
Bug bounty rewards
Branded rewards received from companies as part of bug bounty and responsible disclosure programs.